Your software product has passed the technical evaluation, pricing discussions are complete, and an enterprise customer is ready to proceed. Then procurement asks for your latest SOC 2 report. There’s no report to hand over.
Australian SaaS companies entering larger markets face an immediate challenge in this situation. Rushing into the wrong assessment may not satisfy the customer’s requirements, and security assurance takes time. Understanding what the buyer expects, and planning backward from the deadline, is where the solution begins.
A calm first step is to find out exactly what was asked for, and by when. Sometimes the request leaves more room than it first appears, so it’s worth asking before assuming.
Start by Learning Which SOC 2 Report Is Required
SOC 2 reports don’t all provide the same level of assurance. The distinction between SOC 2 type 1 vs type 2 matters when responding to enterprise security requirements. Type 1 looks at whether relevant controls are suitably designed as of a particular date. Over a defined period, Type 2 examines both their design and their operating effectiveness.
Type 1 may be accepted temporarily by an enterprise buyer, but many specifically request Type 2, since it provides evidence covering actual operations. Prior to commissioning an examination, confirm with the customer the report type, the required scope, and acceptable reporting dates.
Write the answers down, since the report type, scope, and dates all drive the plan and the budget. If the customer’s requirements are unclear, ask for the exact wording in the contract or the security questionnaire.
Build Your Timeline Around the Observation Period
A SOC 2 type 2 examination cannot be completed simply by preparing documentation and scheduling an auditor. Relevant controls must be operated by the organization throughout the reporting period. For an initial examination, that period may cover three months, while subsequent reports commonly examine longer periods.
Where your business needs to demonstrate access reviews, security training, or change approvals, those activities must happen, and be documented, during the applicable window. Planning backward from a customer deadline helps identify whether the requested report can realistically be delivered on time.
When the deadline can’t be met within the observation period, say so to the customer early. A dated plan is one interim step that some customers are willing to discuss when they hear about the gap early.
Know What You’re Actually Buying
Although SOC 2 does not issue certificates, businesses frequently search for SOC 2 type 2 certification.
A licensed CPA firm performs an independent examination against the applicable AICPA Trust Services Criteria and issues an attestation report. The report covers the assessed system, relevant controls, testing procedures, and the auditor’s opinion.
It’s that document, often shared under a confidentiality agreement, that customers typically review. A SOC type 2 report, too, relates to a specific period in the past. It does not automatically provide assurance about every change made afterward.
Costs to Know About Before You Begin
More than an independent examination fee is involved in SOC 2 preparation. Businesses may need assistance developing policies, conducting risk assessments, preparing evidence, training employees, and arranging security testing.
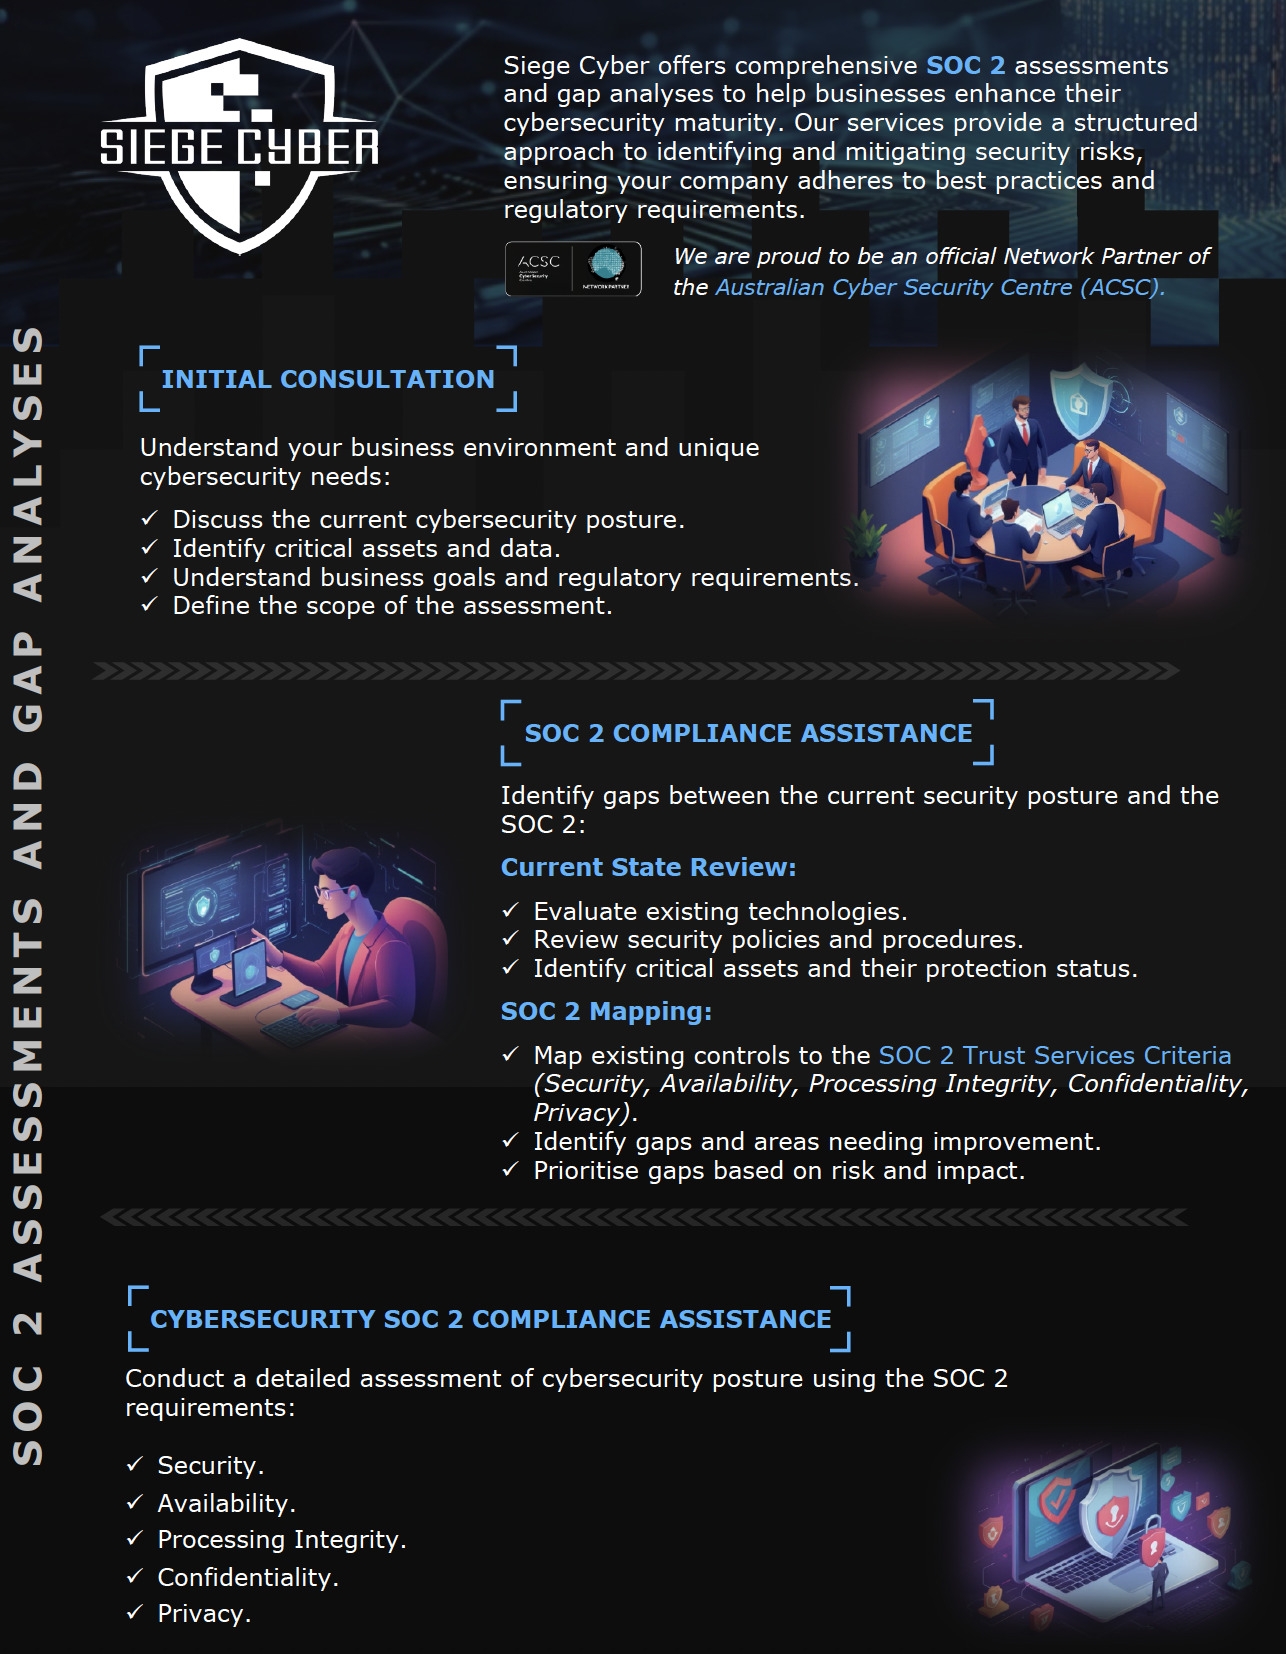
A SOC 2 compliance package priced at AUD $2,750 per month, excluding GST, over twelve months is advertised by Siege Cyber for businesses with up to 50 employees. To be covered by the advertised offer, eligible contracts must be signed by December 31, 2026. Its package includes compliance preparation, training, a compliance platform, and external penetration testing.
Billed separately is the independent CPA examination, with Siege Cyber indicating typical fees of approximately AUD 5,000–15,000, depending on scope and complexity. Make sure you confirm current pricing, eligibility, and deliverables before committing.
Dealing With a Report That Has Aged
Your Type 2 report might cover January through June, and then a customer requests assurance in October. The months in between aren’t examined by the report. A management-issued bridge letter describing relevant changes since the reporting period ended may be acceptable to some customers.
However, acceptance depends on the customer’s requirements, and a bridge letter does not replace an independent examination. Don’t assume an older report will satisfy procurement; discuss reporting gaps early.
Build Compliance That Outlasts One Contract
With fixed-price consulting packages and independent audit coordination, Siege Cyber provides Australian-based SOC 2 readiness support. The most useful approach for growing software companies is to connect compliance preparation with actual operational responsibilities.
Give each control an owner, keep security records, and set a reporting schedule that supports future customer reviews. A successful SOC 2 project should leave your business better prepared for the next enterprise opportunity, not simply help it respond to the current request.
Organized evidence from the start makes the next audit cycle less of a scramble. Review responsibilities and schedules regularly so controls keep operating between audits.